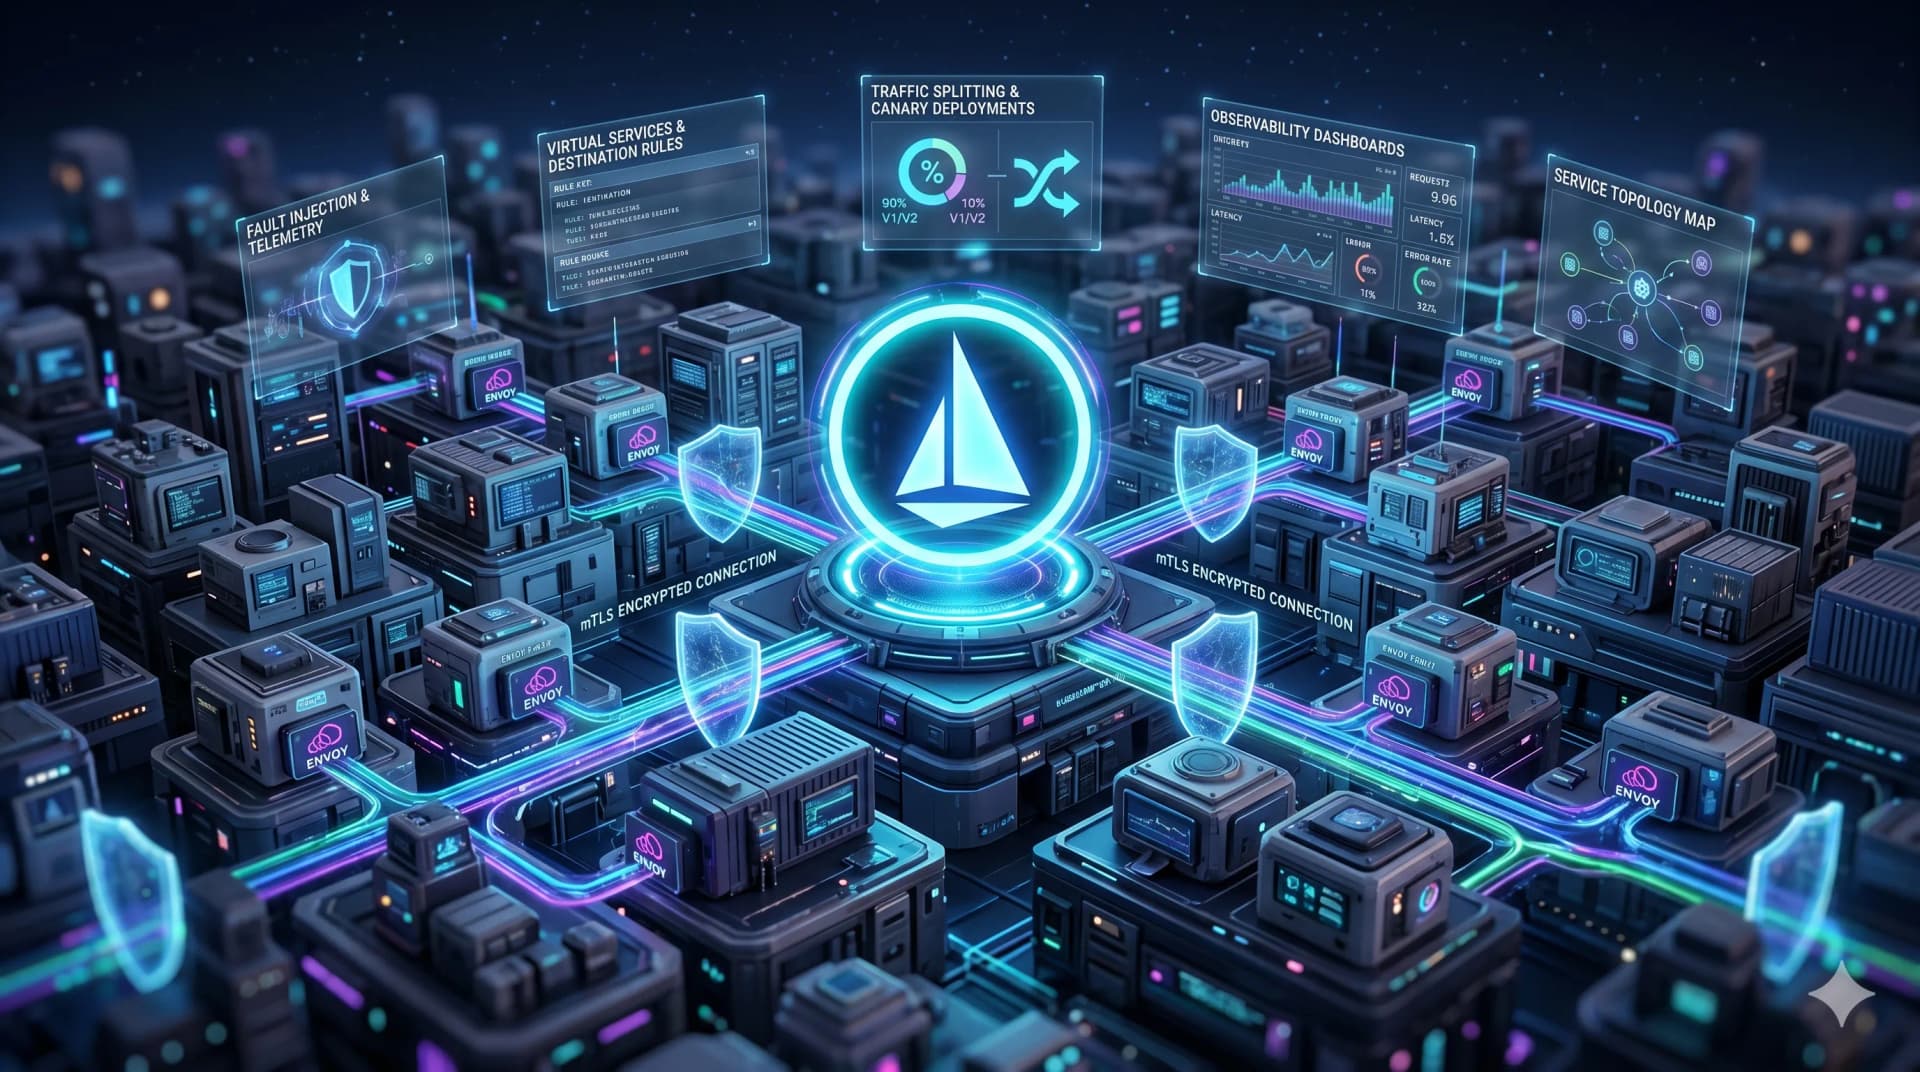
Service Mesh with Istio in Production: Envoy Sidecars, Mutual TLS, Canary Traffic Shifting, and L7 Observability
Lead Cloud Solutions Architect
 17 min read
Production guide to Istio Service Mesh on Kubernetes. Master zero-trust mTLS encryption, canary deployments, and Ambient Mesh architecture.
Why Large Kubernetes Clusters Require a Service Mesh
As enterprise engineering organizations grow from 5 to 50+ microservices on Kubernetes clusters, operational complexity explodes. Managing traffic routing, zero-trust encryption, rate limiting, and observability across polyglot microservice teams (written in Go, Node.js, Python, and Java) through application-level libraries leads to duplicated code, inconsistent timeout policies, and severe security compliance vulnerabilities.
A Service Mesh solves this problem by decoupling networking logic from application code, delegating traffic management to transparent Envoy L7 sidecar proxies. Among service mesh solutions, Istio is the industry standard for production enterprise deployments, providing out-of-the-box mutual TLS (mTLS) cryptographic encryption, fine-grained canary traffic shifting, fault injection, and end-to-end distributed tracing.
At Betadrix, our DevOps and SRE consulting team deploys enterprise service meshes. In this deep architectural guide, we dissect the internal control plane mechanics of Istio (istiod), configure zero-trust mTLS encryption policies, implement weighted canary traffic splitting, and analyze production Envoy proxy failure modes. For multi-cluster scaling, explore our guide on Kubernetes multi-cluster management strategies and our cloud consulting services.
Istio Service Mesh Architecture: Control Plane (istiod) vs. Data Plane (Envoy)
Below is the production topology of Istio managing ingress and inter-service communication across Kubernetes worker nodes:
+-------------------------------------------------------------------------------+
|                       ISTIO SERVICE MESH PRODUCTION TOPOLOGY                  |
+-------------------------------------------------------------------------------+
[External Internet Traffic]
       |
       | HTTPS (Port 443) / mTLS
       v
+-------------------------------------------------------------------------------+
| [Istio Ingress Gateway] (Envoy Proxy at Cluster Edge)                         |
|  - Edge TLS Termination & Wildcard Certificate Management                     |
|  - Ingress VirtualService Path Routing (/api/v1/*, /checkout/*)               |
|  - Global Rate Limiting & Web Application Firewall (WAF) Integration          |
+-------------------------------------------------------------------------------+
       |
       | Automatic mTLS SPIFFE/SPIRE Mutual Authentication
       v
+-------------------------------------------------------------------------------+
| [Kubernetes Pod: Frontend Service]                                            |
|  +--------------------+  localhost:15001  +---------------------------------+  |
|  | [App Container]    | <===============> | [Envoy Sidecar Proxy (istio-proxy)]|
|  | - Node.js Fastify  |   (Zero Code Chg) | - Intercepts Inbound/Outbound   |  |
|  +--------------------+                   | - Enforces mTLS & Timeout (2.5s)|  |
|                                           +---------------------------------+  |
+-------------------------------------------------------------------------------+
       |
       | WireGuard / mTLS Encrypted Overlay
       v
+-------------------------------------------------------------------------------+
| [Kubernetes Pod: Order Service (Canary Split)]                                |
|                                                                               |
|  +----------------------------------------+                                   |
|  | [Envoy Sidecar Proxy]                  |                                   |
|  | - VirtualService: 90% -> v1, 10% -> v2 |                                   |
|  +----------------------------------------+                                   |
|       | (90% Traffic)                         | (10% Traffic)                 |
|       v                                       v                               |
|  +--------------------+                  +--------------------+               |
|  | [Order Service v1] |                  | [Order Service v2] |               |
|  | - Stable Baseline  |                  | - Canary Release   |               |
|  +--------------------+                  +--------------------+               |
+-------------------------------------------------------------------------------+
       ^
       | Configuration Synchronization (xDS Protocol: LDS, RDS, CDS, EDS)
+-------------------------------------------------------------------------------+
| [Istio Control Plane: istiod]                                                 |
|  - Pilot: Translates Kubernetes CRDs into Envoy xDS Configurations            |
|  - Citadel: Issues SPIFFE X.509 Certificates (Rotated Every 24 Hours)         |
|  - Galley: Validates Declarative Istio YAML Manifests                         |
+-------------------------------------------------------------------------------+
Zero-Trust Security: Enforcing Strict Mutual TLS (mTLS)
By default, Istio operates in PERMISSIVE mode to allow gradual migration. In enterprise production, we enforce STRICT mTLS across the entire cluster, ensuring that any unencrypted plain-text communication is immediately dropped at the network packet level:
# strict-mtls-peer-authentication.yaml
apiVersion: security.istio.io/v1beta1
kind: PeerAuthentication
metadata:
  name: default
  namespace: istio-system
spec:
  mtls:
    mode: STRICT
---
# authorization-policy.yaml: Restrict Order Service access strictly to Frontend
apiVersion: security.istio.io/v1beta1
kind: AuthorizationPolicy
metadata:
  name: order-service-rbac
  namespace: production
spec:
  selector:
    matchLabels:
      app: order-service
  action: ALLOW
  rules:
    - from:
        - source:
            principals: ["cluster.local/ns/production/sa/frontend-service-account"]
      to:
        - operation:
            methods: ["POST", "GET"]
            paths: ["/api/v1/orders/*"]
Canary Traffic Shifting with VirtualService & DestinationRule
Istio allows fine-grained percentage-based canary deployments without modifying DNS records or restarting pods. The following configuration splits traffic 90% to stable v1 and 10% to canary v2:
# destination-rule.yaml: Defines service subsets
apiVersion: networking.istio.io/v1alpha3
kind: DestinationRule
metadata:
  name: order-service-subsets
  namespace: production
spec:
  host: order-service.production.svc.cluster.local
  subsets:
    - name: v1
      labels:
        version: v1.14.2
    - name: v2
      labels:
        version: v2.0.0-canary
---
# virtual-service.yaml: Traffic percentage shifting
apiVersion: networking.istio.io/v1alpha3
kind: VirtualService
metadata:
  name: order-service-canary
  namespace: production
spec:
  hosts:
    - order-service.production.svc.cluster.local
  http:
    - route:
        - destination:
            host: order-service.production.svc.cluster.local
            subset: v1
          weight: 90
        - destination:
            host: order-service.production.svc.cluster.local
            subset: v2
          weight: 10
      timeout: 3.0s
      retries:
        attempts: 3
        perTryTimeout: 1.0s
        retryOn: '5xx,connect-failure,refused-stream'
Performance Benchmarks: Envoy Sidecar Latency & Memory Footprint
| Service Configuration | p50 Roundtrip Latency | p99 Roundtrip Latency | Memory Overhead / Pod |
|---|---|---|---|
| Bare Kubernetes (No Mesh) | 1.8ms | 8.2ms | 0 MB |
| Istio Sidecar (mTLS Enabled) | 2.9ms (+1.1ms) | 12.4ms (+4.2ms) | 45 MB RAM / proxy |
| Istio Ambient Mesh (Sidecarless) | 2.1ms (+0.3ms) | 9.6ms (+1.4ms) | Shared ztunnel on Node |
Real-World Production Failure Modes
- Envoy Sidecar Memory Explosion from Unfiltered xDS Updates: In a 2,000-pod cluster, every single pod change generates xDS configuration updates to all Envoy proxies. Without tuning, each Envoy proxy consumes over 1.2GB of RAM. Mitigation: Deploy
SidecarCRDs in every namespace to restrict proxy visibility strictly to services they actually communicate with. - Pod Startup Race Condition (App Starts Before Envoy): When a containerized application boots faster than the
istio-proxycontainer, initial database connections or external API calls fail because iptables routes traffic to an unready proxy. Mitigation: EnableholdApplicationUntilProxyStarts: truein Istio pod injection templates. - 503 UC (Upstream Connection Termination) Spikes: Premature TCP connection closure by upstream servers causes transient 503 errors. Mitigation: Configure Envoy idle timeouts to be strictly shorter than application server keep-alive timeouts.
Series Guide
Cloud & DevOps Automation
Explore Categories
Browse More Technical Topics & Industry Guides
?Frequently Asked Questions
What is a Service Mesh and why is Istio widely adopted?
How does Istio enforce mutual TLS (mTLS) between microservices?
What is the difference between VirtualService and DestinationRule in Istio?
How much latency does an Envoy sidecar add to request roundtrips?
What is Istio Ambient Mesh?
How do you observe microservice traffic in Istio?
Shivam Sharma
Lead Cloud Solutions ArchitectShivam Sharma is an AWS Certified Solutions Architect specializing in cloud infrastructure, high-availability microservices, and database performance tuning for scalable web clients.
Build Your Custom Project
Connect with technical architects for scope and estimation.
More Articles in DevOps




Related services built to solve your specific challenges

Watch.
Learn.
Grow.
Discover how our engineered solutions transform industries and propel client operations forward.
Owning the Game, Not Renting It: Custom Crash Game Development for a Lahore-Based iGaming Operator
READ CASE STUDY
Technologies & Frameworks Powering This Service


Hire Specialized Developers For Your Service Project
React Developers
Pre-vetted senior React Developers ready to deploy into your existing architecture in 3-7 days.
Flutter Developers
Pre-vetted senior Flutter Developers ready to deploy into your existing architecture in 3-7 days.

Nodejs Developers
Pre-vetted senior Nodejs Developers ready to deploy into your existing architecture in 3-7 days.

Python Developers
Pre-vetted senior Python Developers ready to deploy into your existing architecture in 3-7 days.
What Our Clients Say
“Mobile app development and cloud migration were handled smoothly. Strong technical skills, clear communication, and dependable post-launch support stood out throughout the engagement.”
Sarah Mitchell
Director of Operations, HealthFirst Clinics
Have a Project in Mind?
Let's Build It Together.
Connect directly with our senior software architects and technical leads. We evaluate your requirements and deliver an actionable technical proposal within 24 hours.
Strict NDA Protection
Your intellectual property and technical specs remain 100% confidential.
24-Hour Response Guarantee
Guaranteed evaluation and scoping reply from an engineering manager.
Zero Obligation Estimate
Get accurate cost breakdowns and tech stack recommendations free of charge.
Request Free Technical Consultation
Let's build something serious.
Diagnose your system architecture, budget ranges, and roadmap parameters with an expert.
Scoping Diagnostic
Analyze your workflows in 60 seconds. A senior AI architect reviews every parameter personally.
 4.9/5.0 Partner
 4.8/5.0 Leader
 4.9/5.0 Rated
 4.8/5.0 Excellent
Not sure where AI actually moves the needle for you?
Answer a few brief questions. We will deliver a highly concrete scoping plan within 24 hours including:
- Recommendations on automation use-cases and MVP components
- Calculations on expected ROI and engineering timelines
- A structural roadmap to make your legacy stack AI-native